
IDENTOS unlocks safe AI and zero-trust access
Establish policy-based access control (PBAC) guardrails for access, identity, consent decisions and enforce them intelligently
Established in Toronto, IDENTOS was built to solve Canada's hardest identity challenges, governing access inside Canadian health and government programs for over a decade, certified, and audited.
12 years
Delivering production-scale authorization IP for sensitive Canadian data, across provincial health networks, federal identity programs, and regulated private-sector institutions.
ISO 27001 · SOC 2 Type II
Independently certified information security, with controls audited over time, not at a single point in time.
We have spent over a decade embedded in health and government systems, where consent is law and delegation is real, and a wrong access decision has real consequences. PolicyArc is what we've learned, made reusable.
Certified & recognized
New services, new partners, new AI agents, and each one arrives with its own access question, while privacy law, audit expectations, regulatory penalties, and public trust stay unforgiving.
Access rules written into individual applications can't keep up. Security and compliance have to hold as the landscape changes, not be rebuilt every time it does.
Autonomous systems need scoped, revocable access — not a service account with the keys to everything.
People, delegates, and services arrive with credentials from many issuers — and every one of them still needs the right level of access.
Consent, purpose limitation, and the right to withdraw only mean something if they are enforced at the moment data is requested.
Regulators and the public expect a defensible answer for who saw what, when, and on whose authority.
GDPR penalties run past $23M — defensible, auditable access control isn't optional anymore.
Vendors, partners, and contractors all need access. RBAC alone can't govern who they are or what they should see.
Move the access decision out of every application and into one place, and the same work stops repeating across teams, partners, and audits.
New applications inherit access rules instead of rebuilding them, so launches turn on configuration rather than code.
Every decision is recorded with the policy and consent that produced it — an audit trail regulators can follow.
People see what they have shared and can change it, and their directives take effect on the next request.
One policy update reaches every connected service, instead of a release cycle for each team that holds data.
See how we've leveraged our platform to offer identity, consent, and privacy as a user-friendly solution
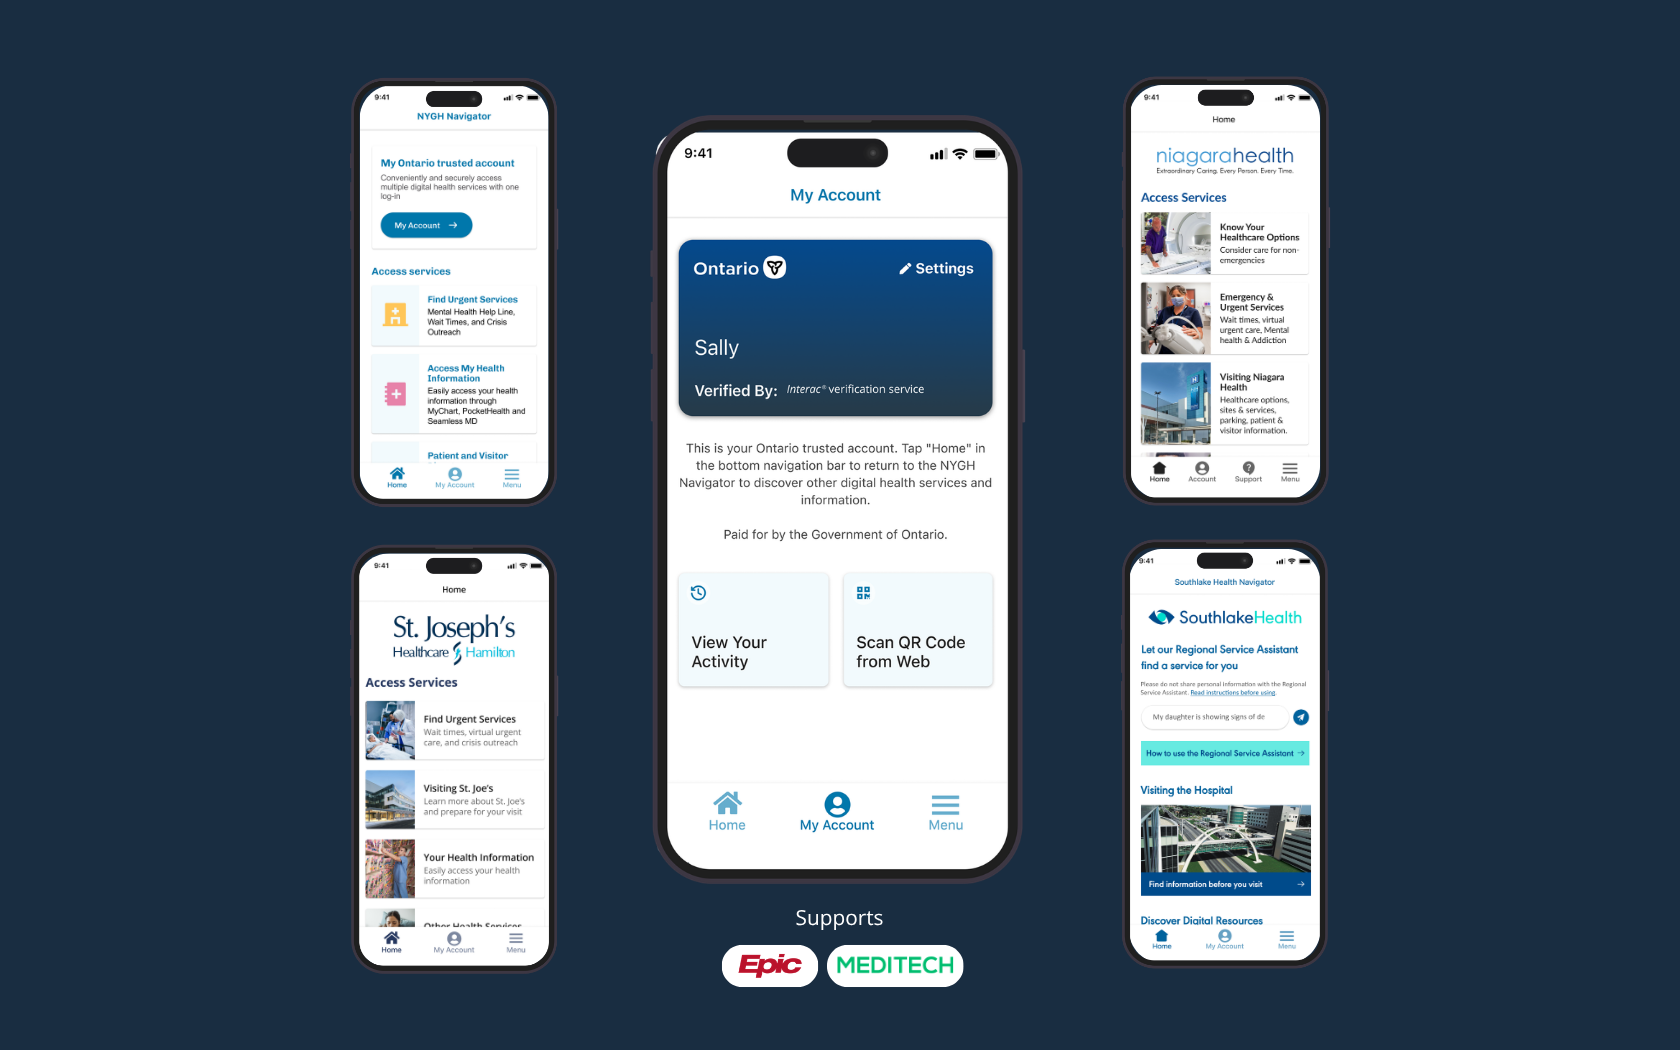
Featured
Digital Identity
A core part of the team behind the Ontario trusted account, IDENTOS extends expertise and tools to scale patient access for Ontarians.
View the case studyThe only PBAC platform where user directives are evaluated on every decision — not filed away after sign-off.
OAuth 2.0 in, one auditable decision out. Harmonize RBAC, ABAC, ReBAC, and TBAC without rewriting your stack.
IAM agnostic and compatible with any identity provider. No rip-and-replace required.
ISO 27001 and SOC 2 Type II, deployed in live healthcare and public-sector programs.
"This initiative is an important step towards a Digital Identity for all Ontarians."
Peter Bethlenfalvy
Minister Responsible for Digital and Data Transformation
News, webinars, and insights from the teams building consent-driven access.
Our architects will help you map a user-centric security framework that scales across services, agencies, and AI.
Speak with us